To close a port on Windows 10, first find which program is listening on it, then either stop that program or block the port with a firewall rule. Run netstat -ano in an administrator Command Prompt to see open ports and their process IDs, end or disable the program that owns the port, and then create an inbound rule in Windows Defender Firewall with Advanced Security that blocks the port. Blocking the port stops other devices from connecting to it, even if the program starts again later.
These steps also work on Windows 11. The menus look slightly different, but the tools and commands are the same.
What “closing a port” actually means
A port is only “open” when a program is listening on it. That gives you two ways to close it, and it’s best to use both:
| Method | What it does | When to use it |
|---|---|---|
| Stop the program or service | Nothing listens on the port anymore, so it’s closed | You don’t need the program, or it shouldn’t be running |
| Block the port in the firewall | The program may still listen, but outside connections are dropped | You need the program for local use, or you want a safety net in case it restarts |
| Close the port on your router | Stops internet traffic from reaching your PC on that port | You set up port forwarding and no longer need it |
Step 1: Find which ports are open
- Click Start, type cmd, right-click Command Prompt, and choose Run as administrator.
- Type the following command and press Enter:
netstat -ano | findstr LISTENING - Look at the Local Address column. The number after the colon is the port. For example, 0.0.0.0:3389 means port 3389 is open on every network connection.
- Note the number in the last column. That’s the PID (process ID) of the program using the port.
To check a single port, such as 8080, use netstat -ano | findstr :8080. Addresses that start with 127.0.0.1 or [::1] only accept connections from your own PC, so they aren’t reachable from other devices.
Prefer a graphical tool? Open Resource Monitor (type resmon in Start), click the Network tab, and expand Listening Ports. It shows each port with the program’s name.
Step 2: Find and stop the program using the port
- In the same Command Prompt, type
tasklist /fi "PID eq 1234", replacing 1234 with the PID from Step 1. This shows the program’s name. - If the name is svchost.exe, the port belongs to a Windows service. Run
tasklist /svc /fi "PID eq 1234"to see which one. - To end the program right now, open Task Manager (Ctrl + Shift + Esc), click the Details tab, right-click the matching PID, and choose End task. You can also run
taskkill /PID 1234 /F. - To stop it from starting again, uninstall the program in Settings > Apps, or, for a service, open services.msc, double-click the service, set Startup type to Disabled, and click Stop.
Be careful with Windows services. Ports like 135, 139, and 445 are used by core Windows features such as file and printer sharing. Don’t disable services you don’t recognize. Look up the name first, or block the port in the firewall instead, which is easy to undo.
Step 3: Block the port with Windows Defender Firewall
- Click Start, type Windows Defender Firewall with Advanced Security, and open it. You can also press Windows + R, type wf.msc, and press Enter.
- Click Inbound Rules in the left pane.
- Click New Rule in the right pane.
- Choose Port and click Next.
- Select TCP or UDP. Choose Specific local ports and type the port number, such as 3389. You can list several, like 135, 139, 445, or a range, like 5000-5100. Click Next.
- Select Block the connection and click Next.
- Leave Domain, Private, and Public checked so the rule applies on every network, then click Next.
- Give the rule a clear name, like Block TCP 3389, and click Finish.
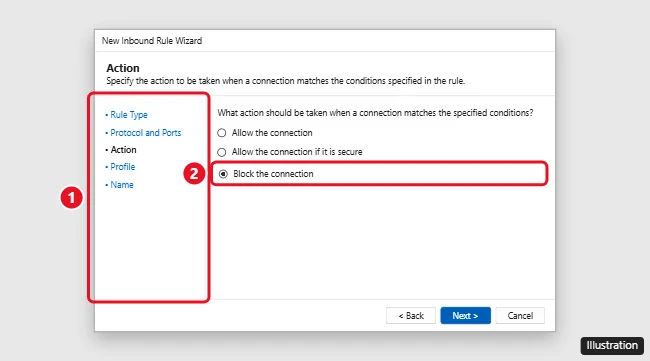
If a program uses both TCP and UDP on the same port, create a second rule for the other protocol. Block rules always win over allow rules in Windows Firewall, so the port stays blocked even if an app added its own allow rule.
You usually don’t need an outbound rule. Outbound rules stop your PC from connecting out on a port, which is a different job from closing a port that others can reach.
Faster option: Block a port with PowerShell
Open PowerShell as an administrator (right-click Start and choose Windows PowerShell (Admin)) and run:
New-NetFirewallRule -DisplayName "Block TCP 3389" -Direction Inbound -LocalPort 3389 -Protocol TCP -Action Block
Change the port number and use -Protocol UDP for UDP ports. To remove the rule later, run Remove-NetFirewallRule -DisplayName "Block TCP 3389".
If you’d rather use Command Prompt, this does the same thing:netsh advfirewall firewall add rule name="Block TCP 3389" dir=in action=block protocol=TCP localport=3389
Step 4: Check that the port is closed
- On the same PC: Run
netstat -ano | findstr :3389again. If nothing shows up, no program is listening, and the port is closed. - From another PC on your network: Open PowerShell and run
Test-NetConnection 192.168.1.20 -Port 3389, using your PC’s IP address. TcpTestSucceeded : False means the port is blocked. - From the internet: Use your router’s port forwarding page to confirm there’s no rule sending that port to your PC.
Close a forwarded port on your router
If you forwarded a port for a game server, camera, or remote access, it’s open to the whole internet, not just your network. Sign in to your router’s admin page (often 192.168.0.1 or 192.168.1.1), find Port Forwarding, Virtual Server, or NAT, and delete the rule. Turning off UPnP in the same settings also stops apps from opening ports on their own.
Ports people commonly close
| Port | Used by | Safe to block? |
|---|---|---|
| 3389 (TCP) | Remote Desktop | Yes, if you don’t use Remote Desktop to connect to this PC |
| 445 (TCP) | File and printer sharing (SMB) | Yes on single PCs. It breaks shared folders and network printers. |
| 135, 137-139 | Windows networking (RPC, NetBIOS) | Usually, on PCs that don’t share files. Test afterward. |
| 5357 (TCP) | Network discovery | Yes, but other PCs won’t see yours in File Explorer. |
| 8080, 8000, 3000 | Local web servers and developer tools | Yes, unless you’re serving something to other devices. |
How to undo it
Open wf.msc, click Inbound Rules, find your rule by name, then right-click it and choose Disable Rule or Delete. If a program stops working after you block a port, this is the first thing to check. To open a port on purpose instead, see how to open ports on Windows 11.
Frequently asked questions
Is it safe to close all open ports?
No. Windows and your apps need some ports to work, and your browser uses temporary ports every time it loads a page. Only close ports you’ve identified and don’t need, especially ones reachable from other devices.
Does Windows Firewall already block ports?
Yes. By default, Windows Firewall blocks inbound connections that don’t match an allow rule. A port becomes reachable when an app or feature adds an allow rule, often when you click Allow access on a firewall prompt. A block rule overrides those.
Why does netstat still show the port after I blocked it?
A firewall rule doesn’t stop the program from listening, so netstat still lists it. The port is closed to other devices, though. To remove it from netstat, stop or uninstall the program.
How do I close a port without admin rights?
You can’t create firewall rules without administrator access. You can still close apps you started yourself in Task Manager, which closes any ports they opened.
Kermit Matthews runs Live2Tech from just outside Philadelphia. He started on a university help desk, spent years as the IT person for small businesses, and has been writing tech guides full time since 2020. Each guide is checked on a device he owns, and re-checked when a menu moves. More about Kermit.