Some apps, game servers and remote tools need an inbound port open in Windows Defender Firewall. You add a rule for the exact port and protocol, and only on the network profiles that need it. Windows 10 reached end of support on October 14, 2025. Consumer Extended Security Updates (ESU) now run until October 12, 2027. The same steps work on Windows 11.
Quick Answer
Open Windows Defender Firewall with Advanced Security, select Inbound Rules, New Rule, choose Port, enter the TCP or UDP port number, choose Allow the connection, pick the profiles and name the rule.
How to Allow a Port Through Windows Firewall
- Press Windows plus R, type wf.msc and press Enter to open Windows Defender Firewall with Advanced Security.
- Select Inbound Rules, then New Rule in the right pane.
- Choose Port and click Next.
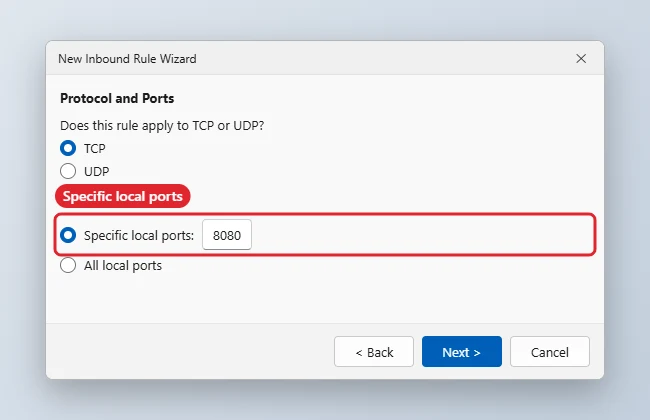
- Pick TCP or UDP, choose Specific local ports and type the port, such as 8080.
- Choose Allow the connection, then select Domain, Private and/or Public. Leave Public unchecked unless you need it.
- Name the rule clearly, such as Game server 8080, and click Finish.
Rule Choices
| Setting | Recommendation |
|---|---|
| Protocol | Match what the app documents (TCP, UDP or both as two rules) |
| Ports | Only the ones you need |
| Profiles | Private for home networks; avoid Public |
| Direction | Inbound for incoming connections |
| Name | Something you will recognize later |
Troubleshooting
- Port still closed: the app itself must be listening, and your router may also need port forwarding. Test with how to check if a port is open on Windows.
- Third-party security suites can have their own firewall. Add the rule there too.
- Rule not applying: check the network is set to Private in Settings, Network and internet.
- For a single game instead of a port, see how to allow Minecraft through the firewall.
Frequently Asked Questions
Is opening a port safe?
It adds risk. Open only what you need, on private networks, and remove rules you no longer use.
Can I do this with PowerShell?
Yes. New-NetFirewallRule with the port, protocol and action parameters creates the same rule.
How do I remove the rule?
Right-click it in Inbound Rules and choose Delete, or Disable Rule to keep it for later.
Do I need an outbound rule?
Usually not. Windows allows outbound traffic by default.
Summary
- Open wf.msc.
- Inbound Rules, New Rule, Port.
- Choose protocol and port.
- Allow the connection on the right profiles.
- Name it and finish.

Kermit Matthews is a freelance writer based in Philadelphia, Pennsylvania with more than a decade of experience writing technology guides. He has a Bachelor’s and Master’s degree in Computer Science and has spent much of his professional career in IT management.
He specializes in writing content about iPhones, Android devices, Microsoft Office, and many other popular applications and devices.