A TPM (Trusted Platform Module) is a security chip, or a feature built into your processor, that stores encryption keys for BitLocker, Windows Hello and Secure Boot. It’s also required to upgrade to Windows 11. Most PCs made since about 2016 have one, but it’s often switched off in the BIOS/UEFI settings. This guide shows how to check whether your Windows 10 PC has a TPM, how to get into the firmware settings, and what the setting is called on Intel, AMD and major PC brands.
Quick Answer
Restart into the firmware settings (Settings > Update & Security > Recovery > Advanced startup > Restart now > Troubleshoot > Advanced options > UEFI Firmware Settings > Restart). Find the TPM option, usually under Security, Advanced or Trusted Computing, and set Intel PTT, AMD fTPM or Security Device Support to Enabled. Press F10 to save and exit.
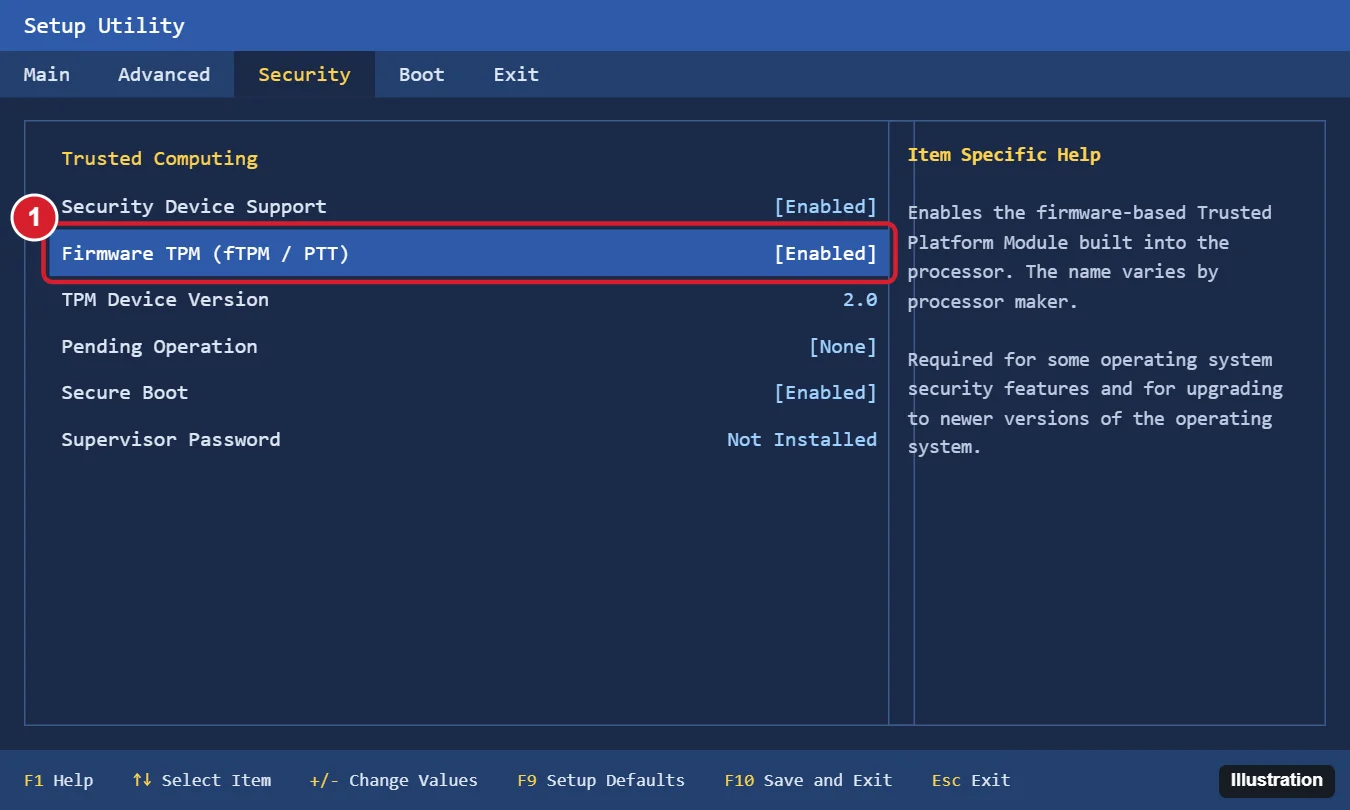
Step 1: Check Whether TPM Is Already On
- Press Windows key + R, type tpm.msc, and press Enter.
- If you see “The TPM is ready for use” and a Specification Version of 2.0, you’re done.
- If you see “Compatible TPM cannot be found”, the TPM is either turned off in the firmware or not present.
You can also check in Windows Security > Device security > Security processor details.
Step 2: Open the BIOS/UEFI Settings
From Windows 10 (easiest on modern PCs):
- Save your work and open Settings > Update & Security > Recovery.
- Under Advanced startup, click Restart now.
- Choose Troubleshoot > Advanced options > UEFI Firmware Settings, then Restart.
With a key at startup: turn the PC on and repeatedly press the setup key, usually Delete or F2 on desktops and most laptops, F10 on HP, F1 on some Lenovo ThinkPads, or Esc for a boot menu. If UEFI Firmware Settings is missing, your PC uses legacy BIOS; use the key method.
Step 3: Enable the TPM
The option’s name and location depend on your processor and PC maker. Look for:
- Intel processors: Intel Platform Trust Technology (PTT), often under Advanced > PCH-FW Configuration, or Security.
- AMD processors: AMD fTPM or AMD CPU fTPM, usually under Advanced > AMD fTPM Configuration, or Settings > Security.
- Dell: Security > TPM 2.0 Security > check TPM On.
- HP: Security > TPM Embedded Security or TPM Device > Available/Enabled.
- Lenovo: Security > Security Chip > Enabled.
- Other boards: Trusted Computing > Security Device Support > Enable.
Select the option with the arrow keys or mouse, change it to Enabled, then press F10 (or go to Exit > Save Changes and Exit). The PC restarts. Some firmware asks you to confirm a TPM change on the next boot; press the key it shows.
Step 4: Confirm in Windows
Run tpm.msc again. It should say the TPM is ready. If you plan to upgrade to Windows 11, run the PC Health Check app to confirm the rest of your hardware qualifies, and check that Secure Boot is enabled too.
Troubleshooting
- No TPM option at all: the PC may be too old (roughly pre-2016) or need a BIOS update. Check the maker’s support site. Some older motherboards have a header for a plug-in TPM module.
- TPM shows version 1.2: some business PCs can be upgraded to 2.0 with a firmware tool from the manufacturer. Windows 11 requires 2.0.
- BitLocker asks for a recovery key after the change: enter the key from your Microsoft account; see how to find your BitLocker recovery key. Suspend BitLocker before changing firmware settings to avoid this.
- “TPM is ready for use with reduced functionality”: clear and reinitialize the TPM from tpm.msc only if you don’t use BitLocker or have your recovery key; see how to clear TPM.
Frequently Asked Questions
Is it safe to turn on TPM?
Yes. Enabling TPM doesn’t change your files or apps, and it improves security. Be careful changing other firmware settings you don’t recognize.
What’s the difference between a TPM chip and firmware TPM?
A discrete TPM is a separate chip on the motherboard; a firmware TPM (PTT or fTPM) runs inside the processor. Both work for Windows 11 and BitLocker.
Do I need to enable TPM to use Windows 10?
No. Windows 10 works without it, but it’s needed for Windows 11, device encryption and some Windows Hello features.
Will enabling TPM slow down my PC?
No. Performance isn’t noticeably affected in normal use.
Summary
- Check with tpm.msc.
- Restart into UEFI Firmware Settings.
- Enable Intel PTT, AMD fTPM or Security Device Support.
- Press F10 to save and restart, then confirm in tpm.msc.

Kermit Matthews is a freelance writer based in Philadelphia, Pennsylvania with more than a decade of experience writing technology guides. He has a Bachelor’s and Master’s degree in Computer Science and has spent much of his professional career in IT management.
He specializes in writing content about iPhones, Android devices, Microsoft Office, and many other popular applications and devices.